The compliance workspace with real people in the loop.
We help you prepare your compliance for GDPR, SOC 2 and ISO 27001.

Good morning, AnnaWhat should we look into?
Sherpa isn’t a chatbot bolted onto a dashboard. It reads your controls, evidence and connected tools — then acts on them inside GRCTrail.
Ask about your controls, vendors, policies or a regulation…
This preview replays scripted conversations — the full agent runs inside your GRCTrail workspace.
Suggested next steps
Based on where your compliance program stands today
Collect a DPA from Google Cloud
It processes production personal data and has no signed agreement.
Turn on branch protection for main
4 automated checks are failing in Source Control.
Complete the quarterly access review
It was last completed 4 months ago.
Trusted by



See the product
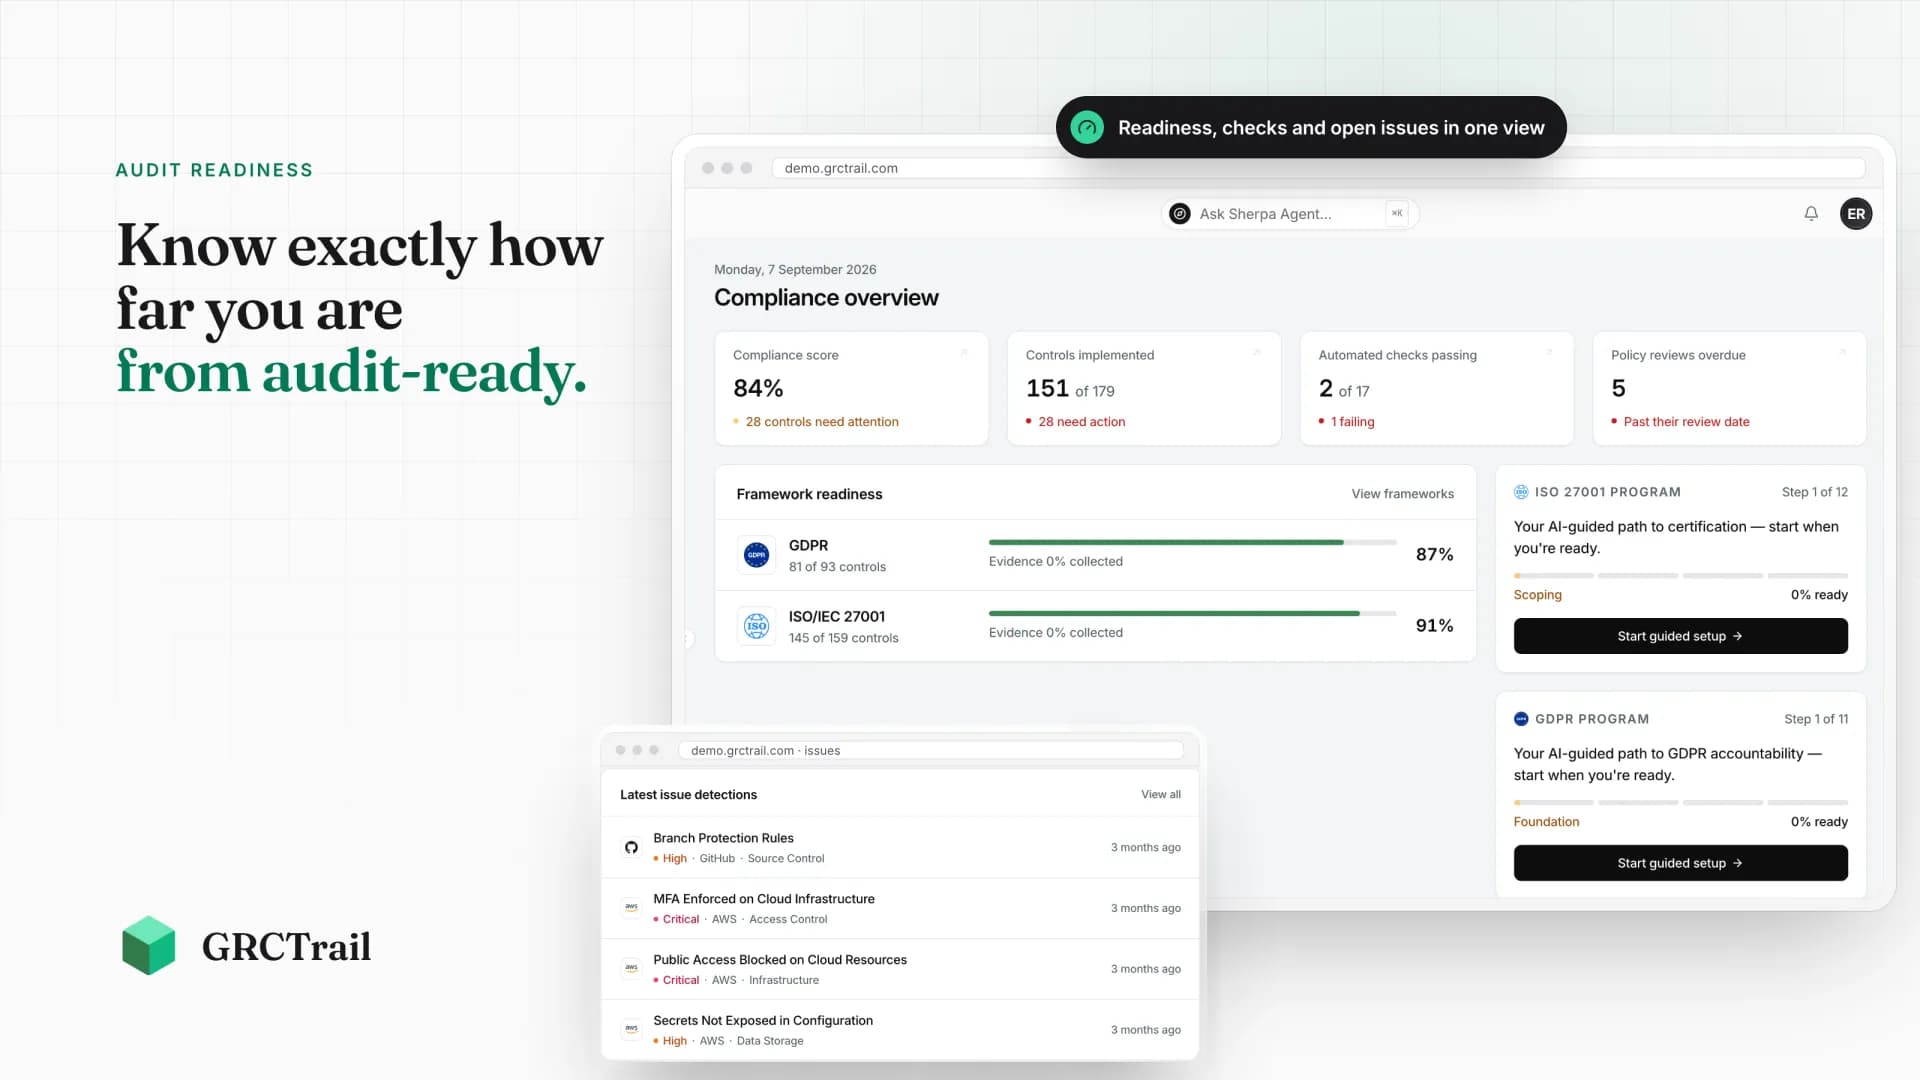
One workspace, every part of the program.
Readiness, policies, evidence, risks, vendors, privacy requests and the tools you already use, all linked to the controls they prove.
One overview for GDPR and ISO 27001: compliance score, controls implemented, automated checks passing and policy reviews due. Every gap has an owner and a next step.
Request accessWhere you stand today
34% ready
- Scope your programDone
- Assign policy ownersDone
- Collect evidence for 12 controlsIn progress
- Book your auditNext
Why GRCTrail
Less compliance work. Not just better-organised compliance work.
Most tools hand you a checklist. GRCTrail's agent drafts policies, collects evidence and maps controls across GDPR, SOC 2 and ISO 27001, so your team reviews instead of writes.
An agent that writes the first draft
Policies, risk register and control mapping generated from how your company actually works.
Evidence collected for you
Connect your stack once. Evidence lands against the right control, continuously.
Answers at any hour
Ask inside the workspace and get a reply that cites your own setup, not a generic help article.
Experts and done-for-you setup
Prefer not to run it yourself? Our certified experts build the programme and get you certification-ready.
Who it's for
Not just software companies. If you hold customer data, this is you.
ISO 27001 and GDPR aren't a SaaS problem. Any business that stores customer data, or sells to companies that vet their vendors, ends up here.
SaaS & software
Enterprise buyers won't sign until you can prove ISO 27001.
Agencies & studios
You hold client data under NDA. They expect it protected.
Fintech & payments
Money and personal data raise the bar; partners and regulators demand proof.
Health & medtech
Patient data is as sensitive as it gets. Privacy is never optional.
IT services & MSPs
You hold the keys to your clients' systems; they audit how you secure them.
E-commerce & marketplaces
Thousands of customers means thousands of GDPR obligations.
HR & recruitment tech
Candidate and employee records are pure personal data. Handle them by the book.
Data & AI companies
Training on personal data puts GDPR and security front and centre.
Not on the list? If you store customer data or answer security questionnaires, ISO 27001 and GDPR will find you too.
Connect your stack
Evidence from the tools you already run.
- AWS
- GitHub
- Vercel
- Slack
- Snyk
- Linear
- Notion
- Okta
- GCP
- Jira
- Supabase
- ClickUp
- Datadog
- Cloudflare
- Azure
- Atlassian
Walk into your next audit prepared.
Request access to the design-partner program, or book a 30-minute call with the founder to see if GRCTrail fits.